
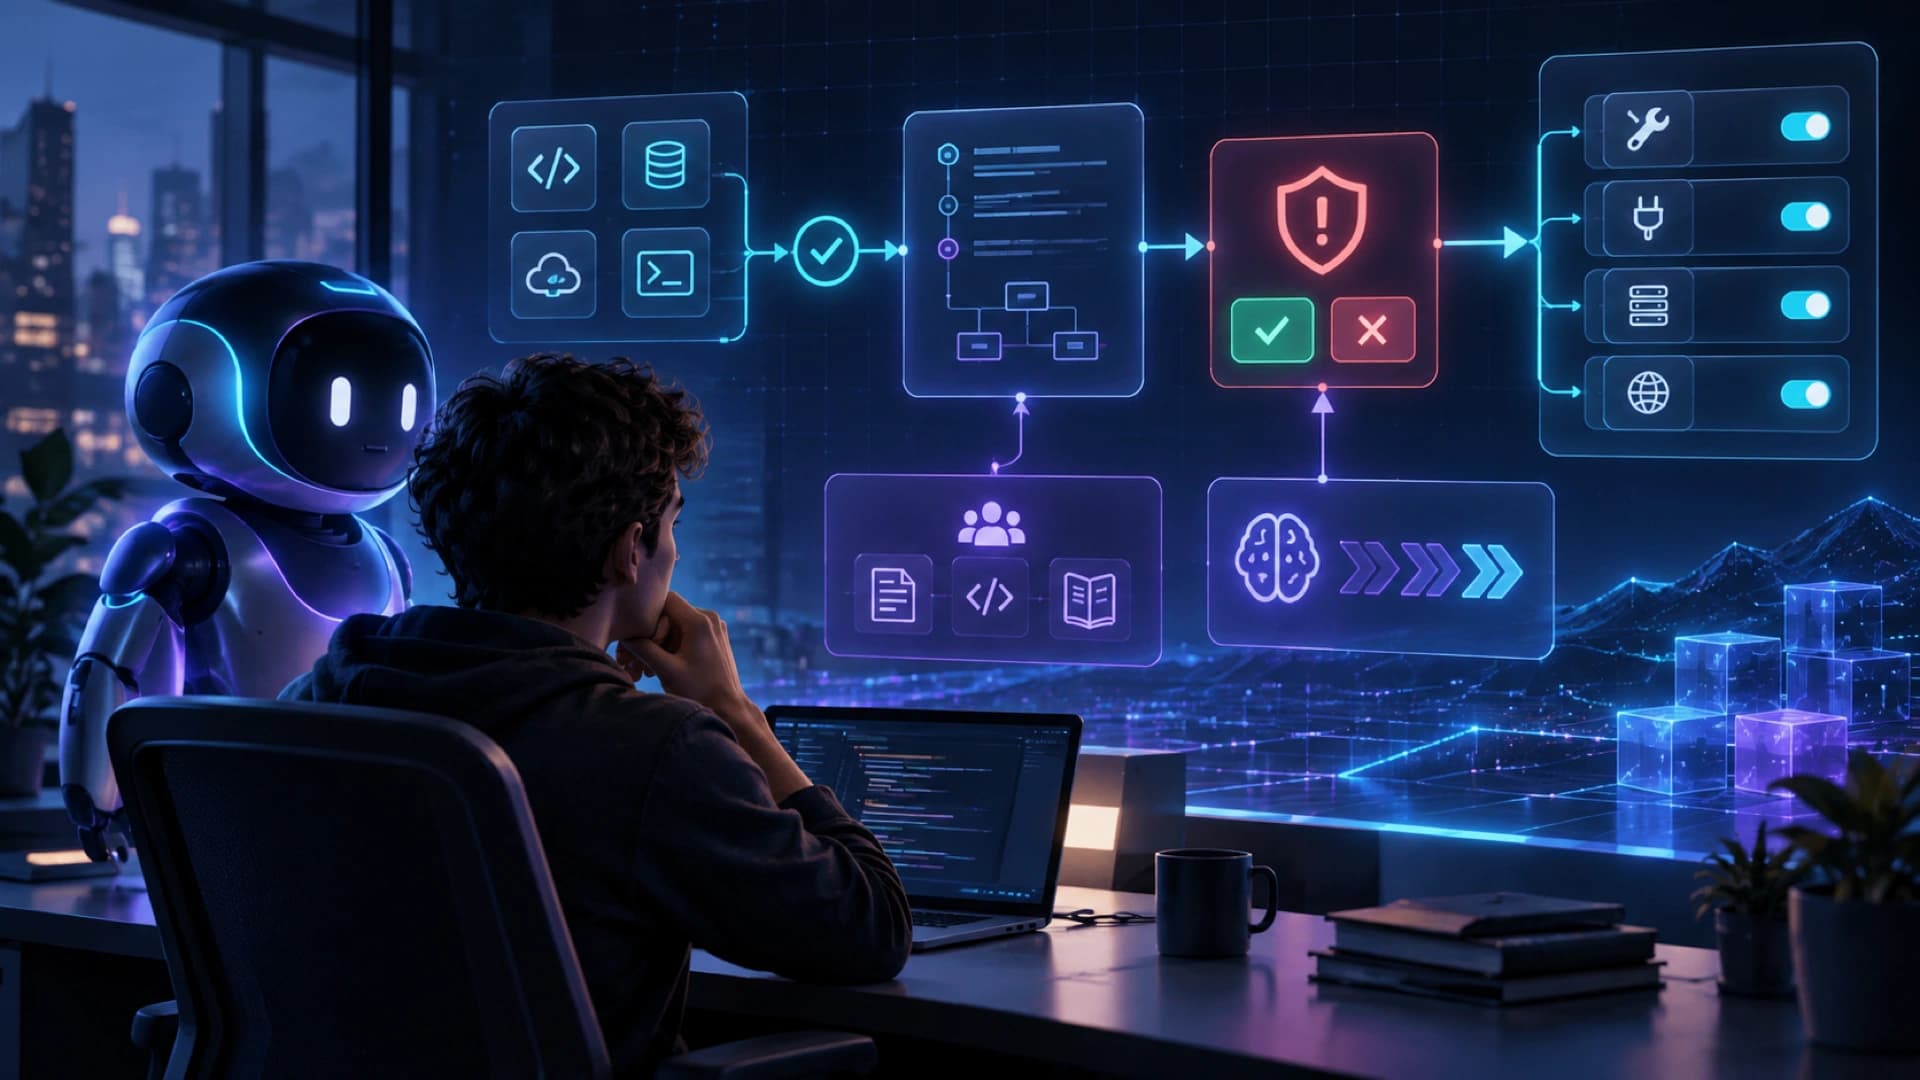
GitHub announced Copilot for JetBrains 1.18.0 on September 22, 2026. The release is less about a new model than about how agent sessions are controlled. It adds AI-assisted tool approvals, re-editing of earlier messages, shared skills and instructions, Codex agent plan mode, and persistent controls for MCP tools.
Assisted approvals are now in public preview. Copilot can attempt to approve low-risk tool calls automatically, while higher-risk actions continue to ask the user for a decision. The tiered model should reduce interruptions for routine reads or searches, but GitHub does not present it as a fully autonomous approval system. Teams still need to define acceptable actions and inspect the permissions behind each tool.
Users can also re-edit an earlier message in an agent session. Before sending the replacement, Copilot rewinds both the conversation and file changes to that point, allowing the user to correct the direction instead of appending another instruction to a broken path. For long-running work, that makes undo part of the workspace state as well as the conversation, which still needs version control and a clear change history.
For organizational management, local and Copilot agent sessions now support organization and enterprise skills together with organization-managed custom instructions. Shared rules can give a team a common baseline for code style, testing, and process. They also create an administrative responsibility: the source, scope, and update lifecycle of those instructions need review so stale guidance does not silently persist.
The Codex agent now supports plan mode. A user can review, refine, or approve a plan before the agent begins implementation. That moves an approval point from an individual tool call to the overall approach, which is useful for large refactors or cross-file changes. A person can inspect the proposed steps, files, and risks before allowing the agent to edit the repository.
On MCP, a new setting can turn the built-in GitHub MCP Server on or off without changing manually configured servers; the built-in server remains enabled by default. Agent sessions also gain persistent per-tool controls for MCP servers. That separates governance of which server is connected from governance of which individual tools inside it are available.
The release puts agent convenience and agent control in the same product surface. Assisted approval reduces friction, plan mode provides a review checkpoint, shared instructions reinforce team standards, and MCP controls narrow the external action boundary. None of these features automatically removes prompt-injection, planning, or permission-configuration risks, so teams still need approval logs, tool reviews, and human oversight.
A sensible rollout is to classify tools and data first, define approval policies second, and only then tune the level of automation. Low-risk reads can be less interruptive, while writes, deployments, deletes, or external communications should retain explicit gates. The important change is the granularity: teams can manage an agent by risk and action rather than by a single all-or-nothing switch.


