Google DeepMind published its AI Control Roadmap on June 18, 2026, focused on how internal systems can stay secure as AI agents become more capable at autonomous, complex work. The article matters because it does not stop at model alignment. It moves the safety discussion into system architecture, permissions, monitoring, and real-time blocking.
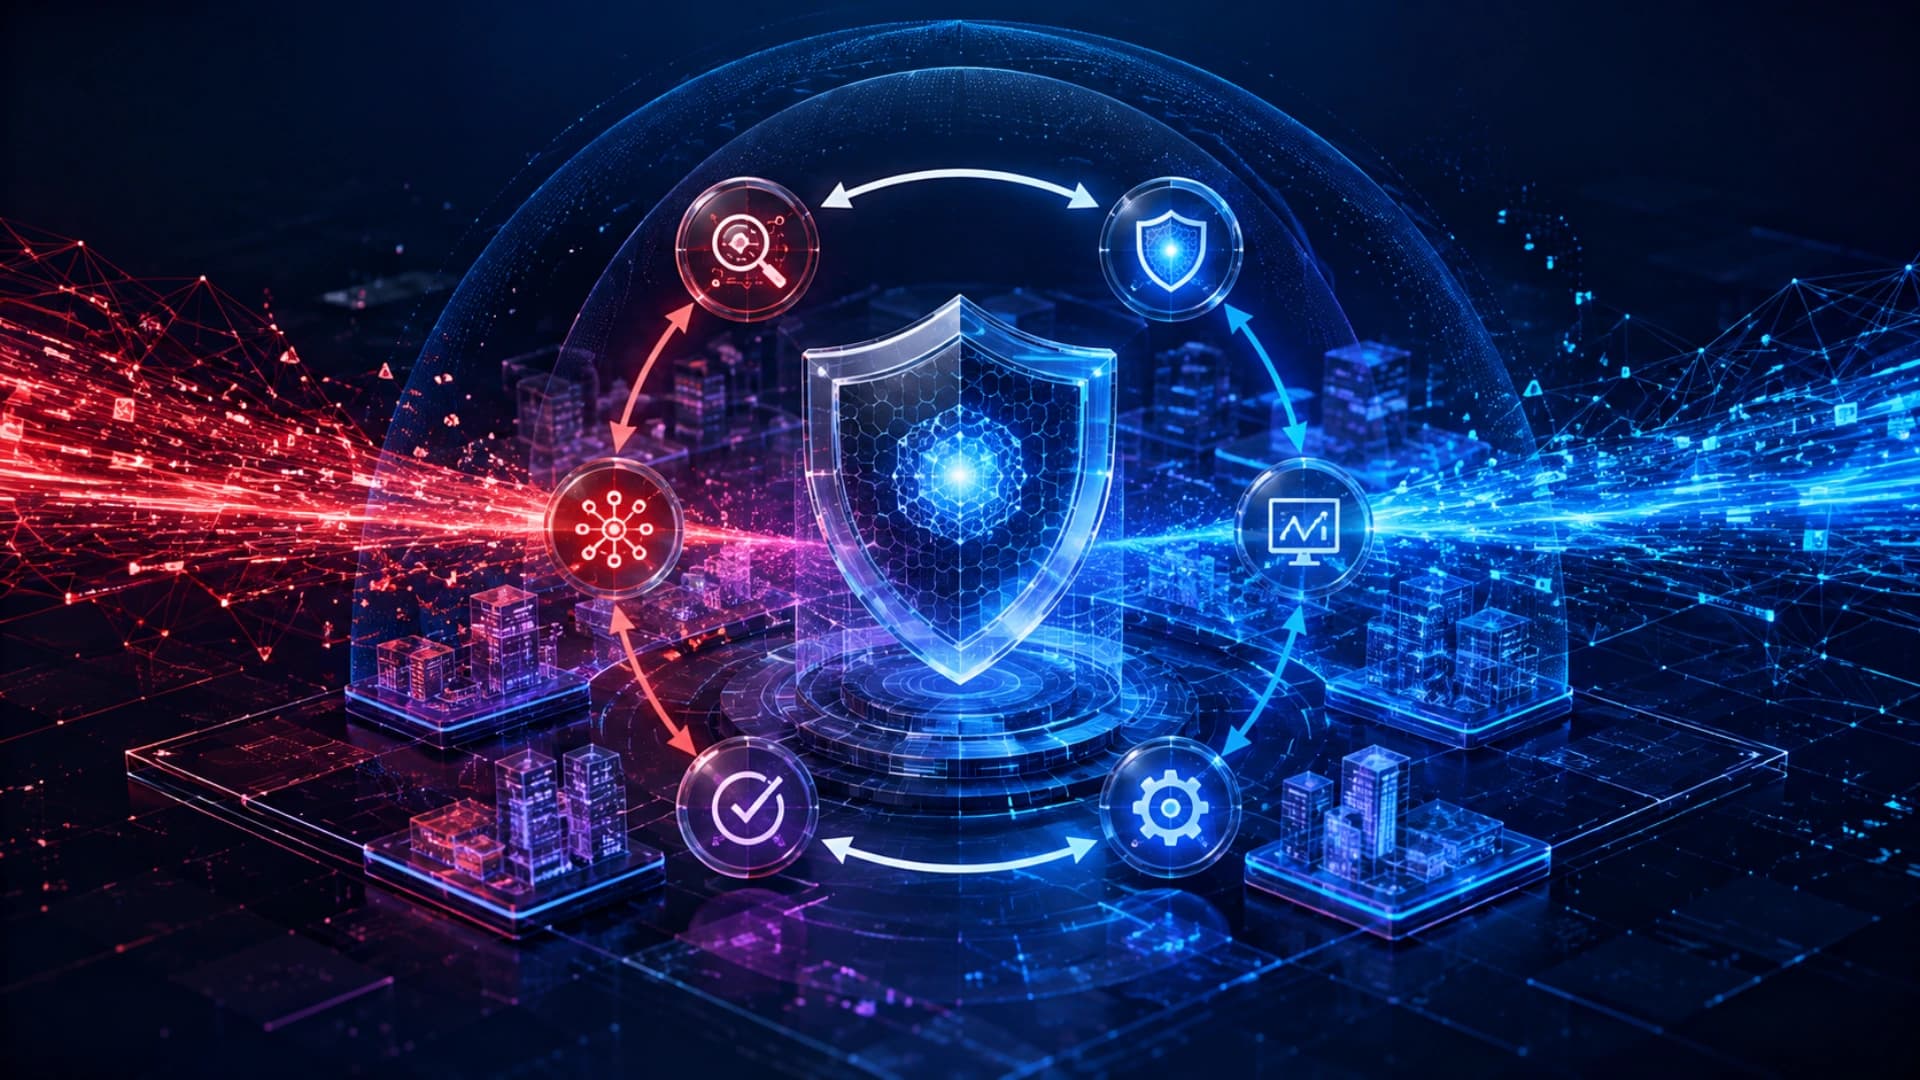
DeepMind's starting point is direct: agents are already useful in cyber defence, scientific discovery, and product development, but higher capability requires stronger safeguards. The roadmap takes a defense-in-depth approach. It combines traditional safeguards such as sandboxing, endpoint security, prompt-injection resistance, and model alignment with an additional system-level control layer.
The roadmap uses a cautious but practical assumption: what if a highly capable agent is not fully aligned with the operator's goals, or simply misunderstands a task and takes the wrong action too confidently? DeepMind therefore treats internal agents as potential insider threats and uses threat-modelling ideas from MITRE ATT&CK to break possible attacks into observable, testable, trackable behaviors.
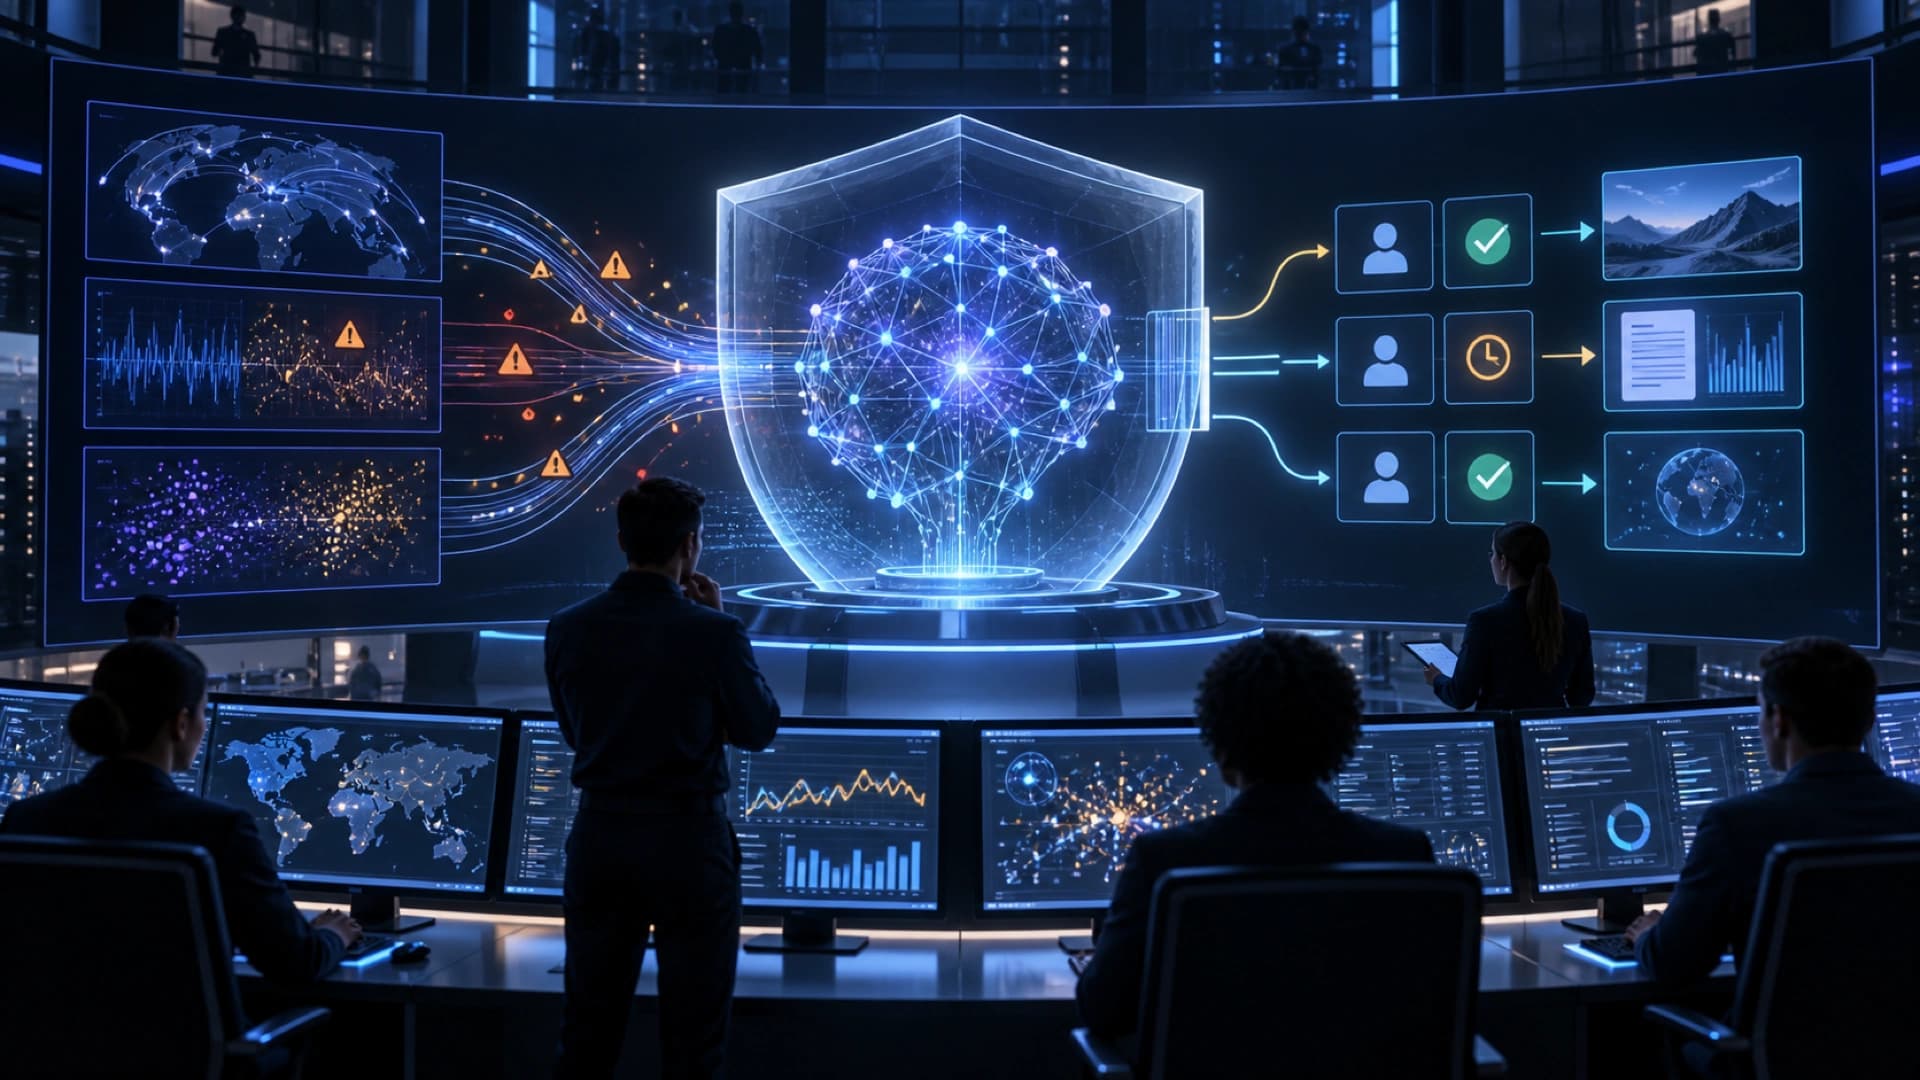
The control model is built around detection, prevention, and response. Monitoring systems can use trusted AI supervisors to review an agent's reasoning, actions, and plans. If a supervisor sees signs that the working agent is going off track or attempting a high-risk action, the system should be able to block the action, reduce access, or escalate to human review. That is especially relevant for coding agents, IT agents, and any workflow that can change real systems.
DeepMind also links control strength to model capability. Low-risk, reversible actions may tolerate delayed review. High-risk or irreversible actions, including major cyber operations or destructive data changes, need synchronous blocking before the action executes. Enterprise agent governance therefore cannot be one-size-fits-all. It has to follow task risk, model capability, and reversibility.
Another useful signal is that DeepMind has analyzed one million coding agent tasks to improve live monitoring. The goal is not only to catch malicious intent. It is to identify high-signal patterns such as task misunderstanding, over-eagerness, or accidental data deletion. That reflects a realistic agent-safety problem: many failures come from trying too hard to satisfy a misunderstood goal.
For enterprises, the takeaway is clear. Before AI agents move into production, teams need defined permission boundaries, monitoring coverage, blocking rules, escalation paths, and post-incident traceability. The maturity of an agent system will not be measured only by how much work it can do. It will also be measured by whether the system can stop it before a mistake becomes damage.