GitHub updated Copilot code review on June 18, 2026 with support for repository-level AGENTS.md files. Teams can now place architecture rules, testing expectations, security checks, naming conventions, and review preferences at the repository root, and Copilot can use the relevant guidance when generating review feedback.
The change looks small, but it matters for AI coding workflows. A common weakness of AI review is not that the model cannot read code at all. It is that the feedback can be too generic. Every codebase has local boundaries: routing conventions, test expectations, data-access patterns, error-handling style, and rules about when to keep a change conservative. AGENTS.md gives those constraints a place to enter automated review.
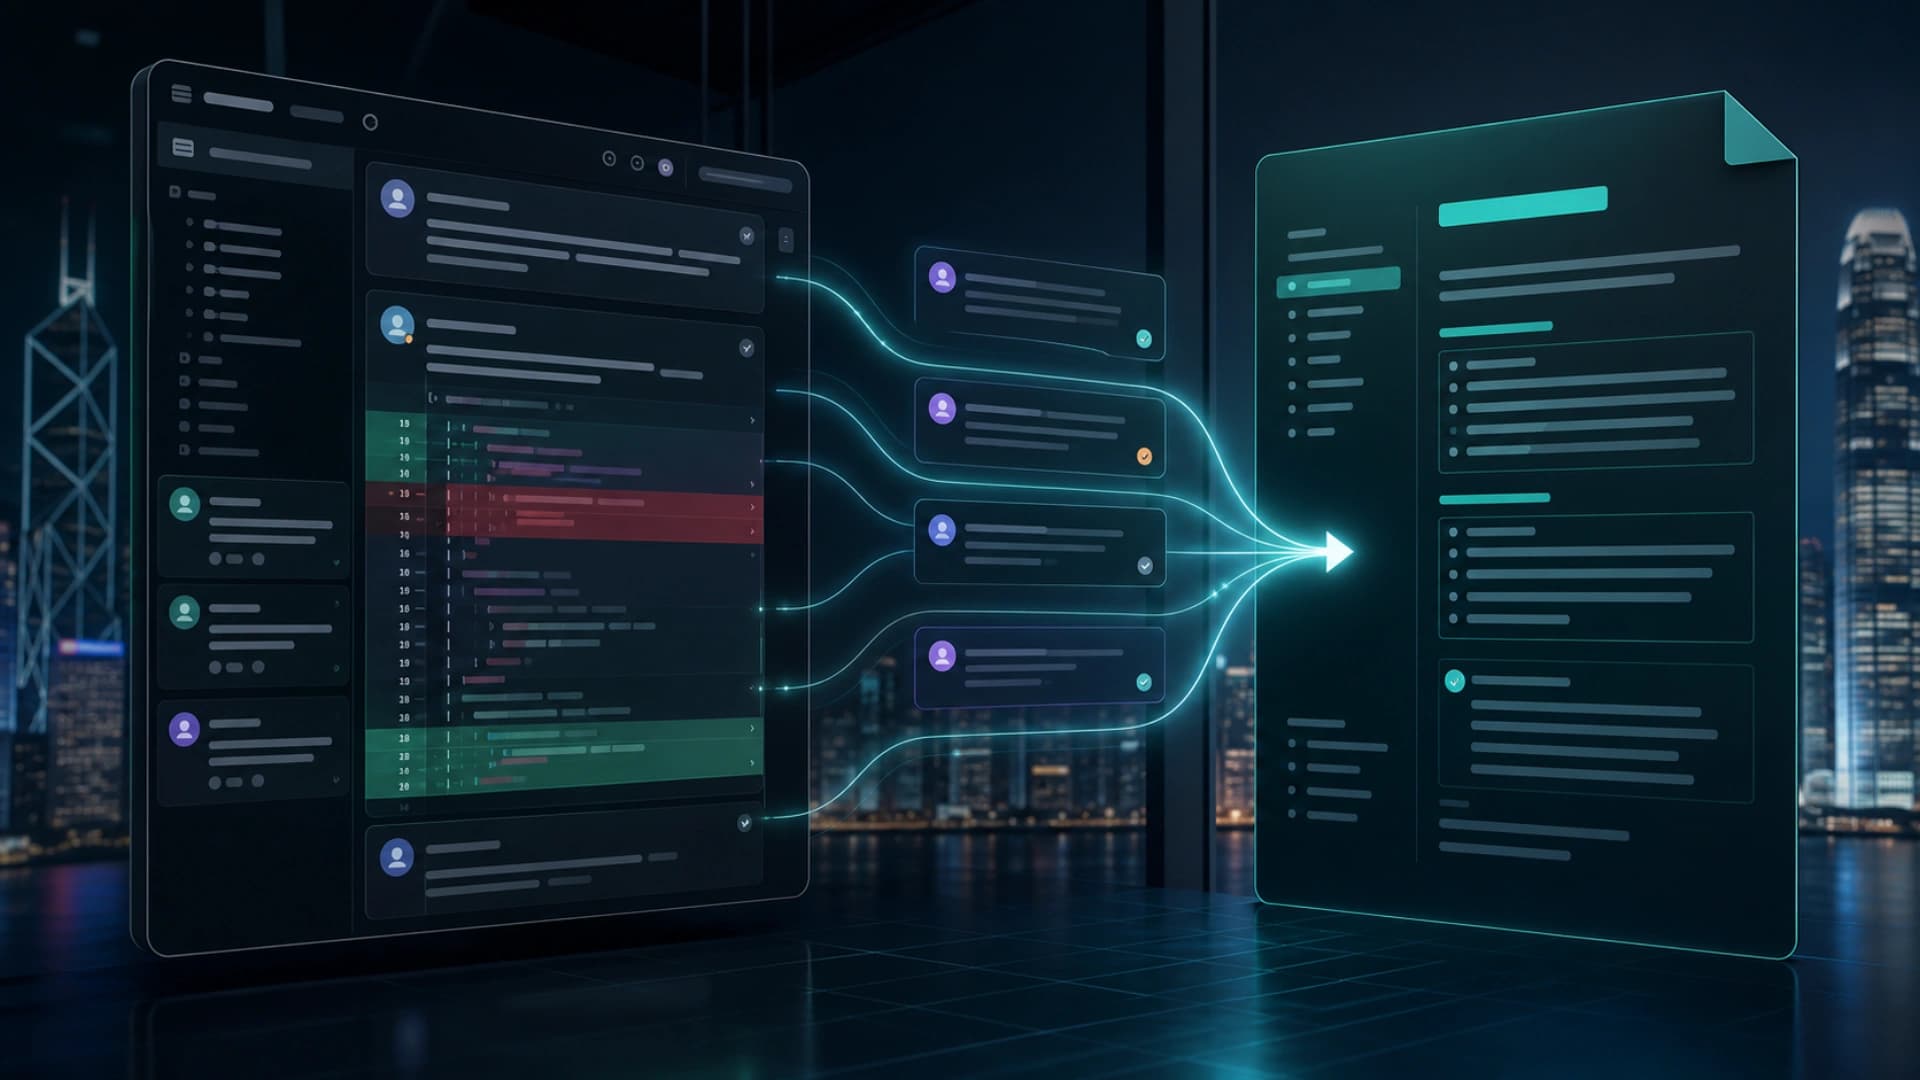
GitHub says Copilot code review now reads AGENTS.md from the repository root and uses relevant instructions from that file. For engineering teams, that is more actionable than leaving rules in a wiki or relying on tribal knowledge. The first review pass can now reflect the standards the team actually wants to enforce.
GitHub also made draft pull request review easier. The Request button now appears next to Copilot, so teams can ask for an automated first pass before a pull request is ready for human review. That is useful in AI-assisted development because many direction-level issues are cheaper to catch while a PR is still a draft.
The UI update that collapses some Copilot review timeline events also matters. If AI review becomes routine, review surfaces need to stay readable. More automation should not make it harder to find the human conversations that still require judgment.
The broader signal is that AI code review is moving from model-only inspection to repository-aware inspection. Teams that want Copilot review to be reliable should not only enable the feature. They should maintain AGENTS.md as a living review context for tests, security, architecture, and product constraints.