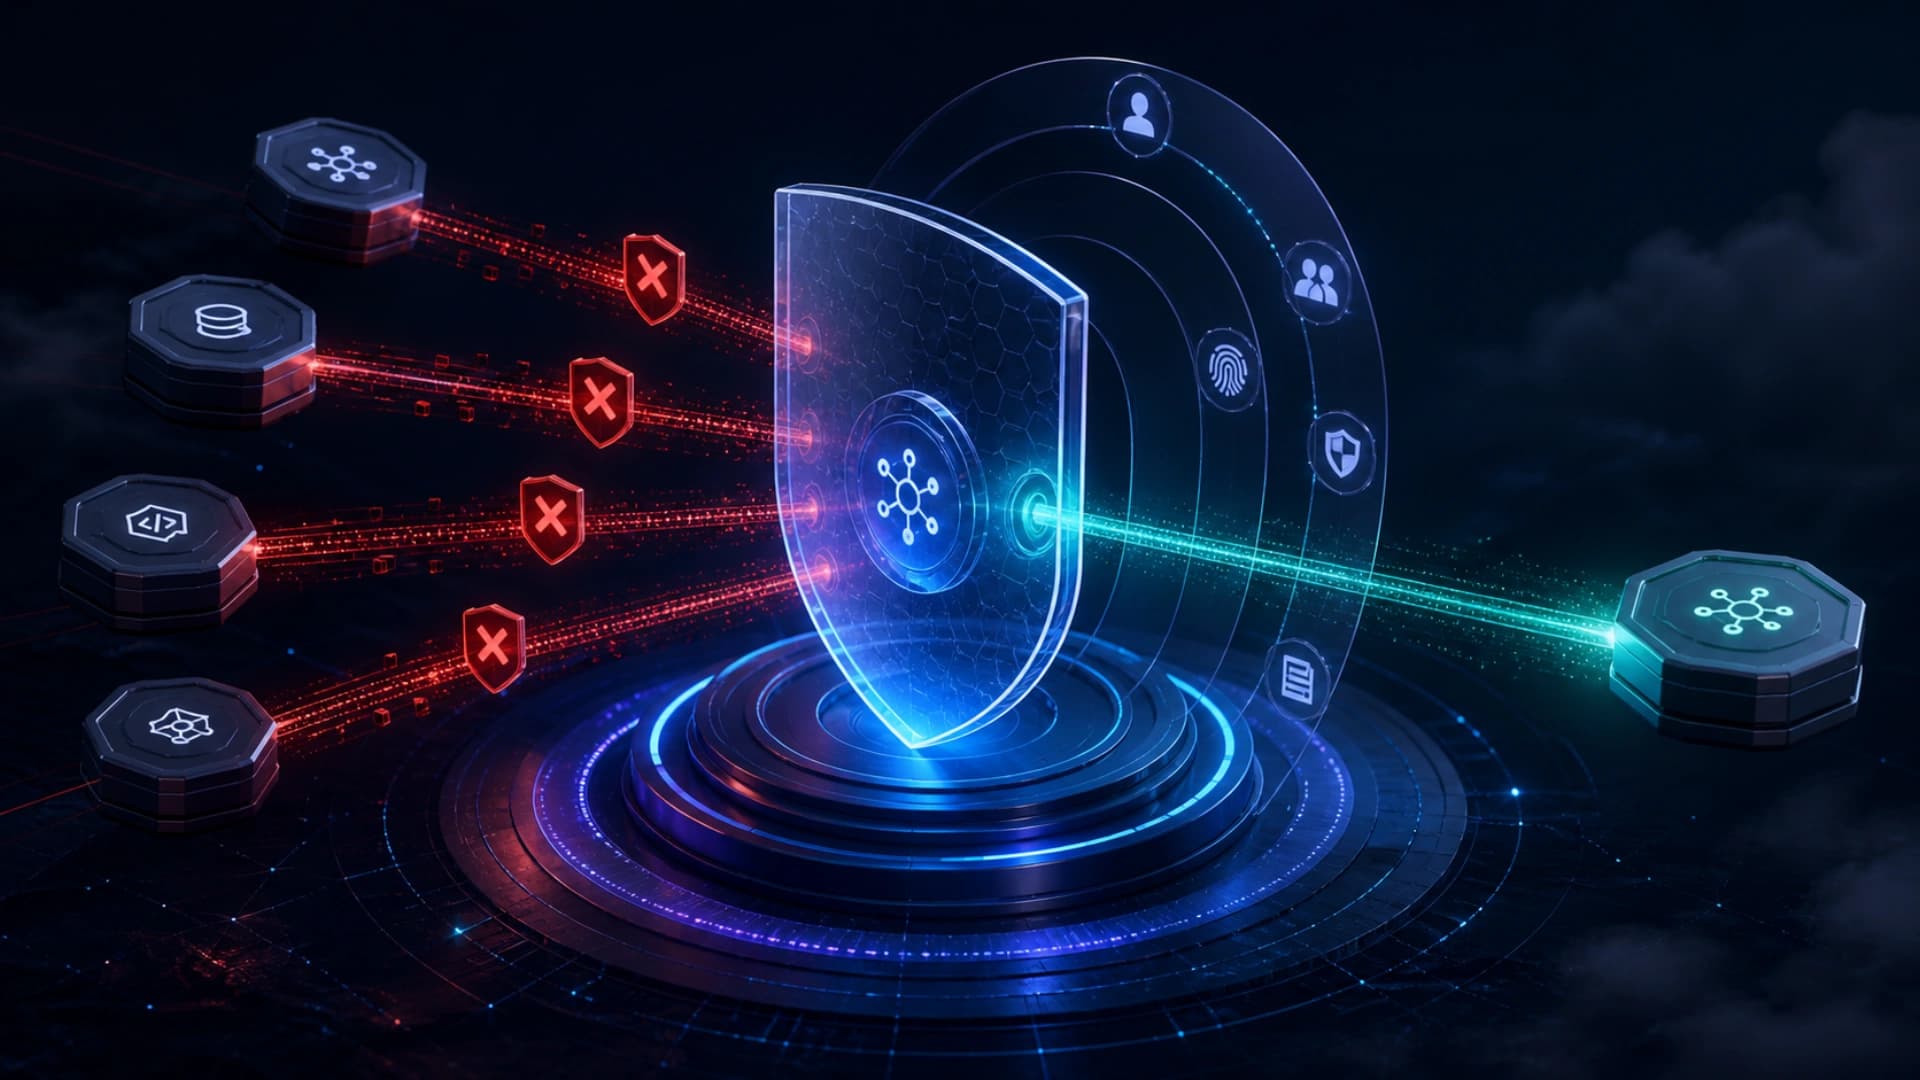
GitHub announced on August 6, 2026 that MCP allowlists in GitHub Copilot enterprise managed settings are generally available. Enterprise owners can centrally control which Model Context Protocol servers Copilot clients are allowed to run and block servers that are untrusted or non-compliant.
The settings live in copilot/managed-settings.json and can use allowedMcpServers, deniedMcpServers, or both. Each matcher can identify an MCP server through serverUrl, serverCommand, or serverName. serverUrl covers remote HTTP/SSE servers and supports wildcards plus URL canonicalization; serverCommand covers local stdio servers by matching the exact command and arguments.
serverName is only a convenience matcher, not a security control, because users can rename a server. That distinction matters: enterprise policy should rely on endpoints or commands that are harder to rewrite, not a label shown in a client interface.
GitHub says the policies fail closed. A malformed or unverifiable configuration blocks the server instead of allowing it under uncertainty. When policies come from multiple layers, the MCP server must pass every layer. This is a conservative enterprise default, but it also means configuration mistakes can make tools unavailable and need to be handled through testing and rollout procedures.
In server-managed deployments, both keys can be marked overridable so enterprise teams can define their own allow and deny lists on top of a baseline. GitHub currently enforces MCP allowlists in the GitHub Copilot app, Copilot CLI, and VS Code.
The setup process also follows repository-based governance. In the source organization’s .github-private repository, an administrator adds the settings and commits them to the default branch. Policies can therefore be maintained through code review, version history, and organization processes instead of relying only on local settings on each developer machine.
Because MCP gives agents access to external data and tools, the value of an allowlist is not only blocking a few servers. It turns “what may this agent use?” into an enterprise policy that can be reviewed. Actual security still depends on precise matchers, trustworthy remote servers, safe local-command dependencies, and tested policy changes. GA provides a centralized control plane, not a security guarantee for every MCP server.
The update shows Copilot agent governance moving from feature configuration toward an execution boundary. As organizations allow multiple agent apps, MCP tools, and clients to coexist, allow, deny, fail-closed behavior, and layered inheritance become conditions that need to be defined before deployment.