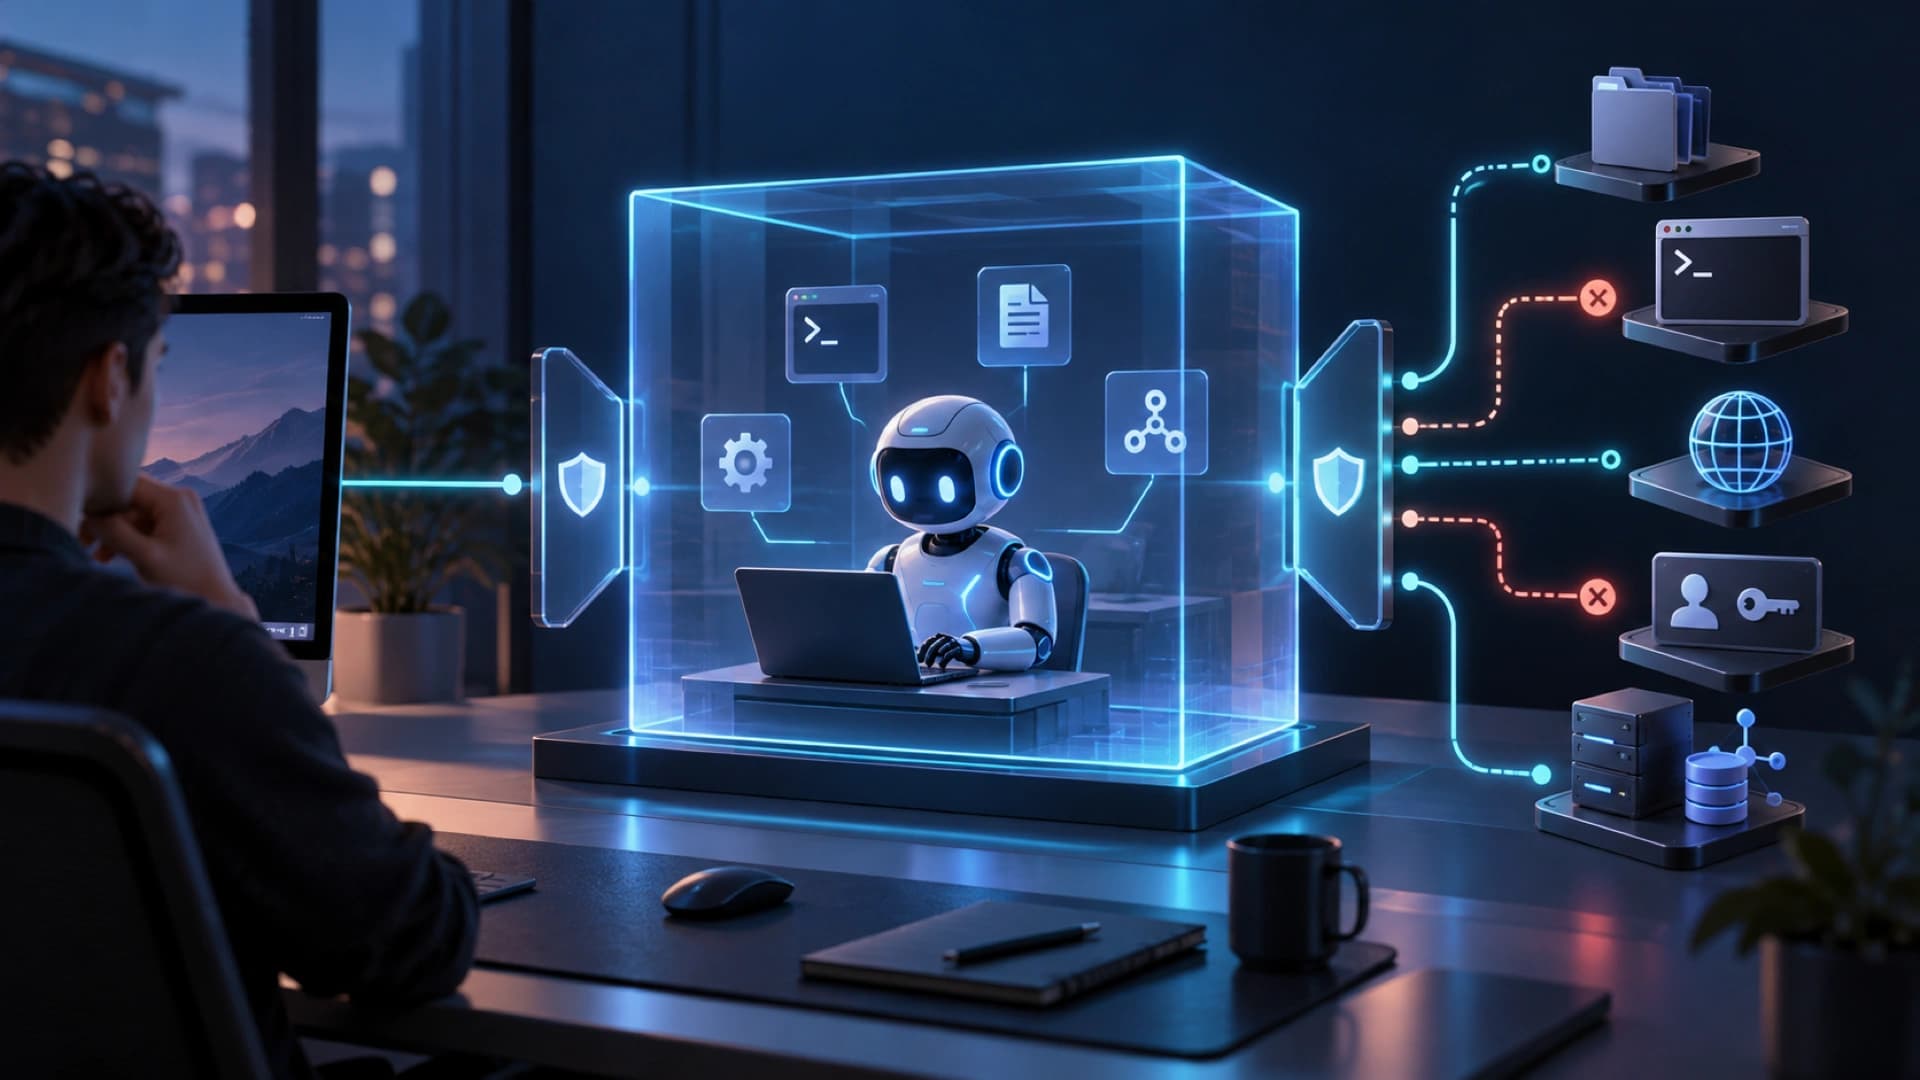
On October 7, 2026, GitHub announced general availability for local sandboxing in GitHub Copilot CLI, the Copilot app, and VS Code sessions that use Agent Host. The feature puts an execution boundary around agentic workflows on a developer’s machine: tools and commands invoked by Copilot are restricted from the filesystem, network, credentials, and other system capabilities according to developer or organization policies.
Local sandboxing is powered by Microsoft eXecution Container, or MXC, which maps a common sandbox policy to native operating-system controls across Windows, macOS, and Linux. The controls can limit which files and directories an agent may read or modify, access to the internet and local networks, Git and GitHub CLI credentials, and, where supported, local MCP servers and language servers.
Enterprise administrators can require sandboxing and enforce policies that developers cannot weaken. GitHub also separates model execution from tool isolation: sandbox policies govern tool execution regardless of which model Copilot uses. Switching models therefore does not automatically bypass the execution layer’s file, network, or credential restrictions.
The design addresses a practical tension in agent workflows. An agent that fixes code, runs tests, or operates local services needs tool access, but broader access increases the impact of a bad command or an unclear prompt. A local sandbox separates what an agent can execute from what it is allowed to reach, so teams can start with narrow file and network policies and expand them deliberately.
A sandbox is not a complete agent-safety guarantee. It does not decide whether a prompt, MCP server, dependency, or workflow is trustworthy, and not every local tool necessarily receives the same level of isolation. Before production use, teams still need to test paths, credentials, network exceptions, operating-system support, and enterprise policy behavior, while preserving approvals and logs for sensitive actions.
GitHub says local sandboxing is included with GitHub Copilot at no additional cost. For agent products, the significance is more than another setting: the question of what an agent may do becomes an organizational execution boundary rather than only a model-capability question. Reliability still depends on policy design, test coverage, and human oversight.